Ecurem CLM
Centralized governance of certificates and cryptographic assets: discovery, inventory, renewal orchestration, compliance, client PKI, crypto-agility and AI-assisted operations.

Ecurem brings visibility, automation and governance to certificates, cryptographic assets, PKI and cryptographic transformation, from day-to-day TLS operations to post-quantum readiness.

Use the SaaS control plane when you need centralized lifecycle governance, and local automation when infrastructure must remain under your control.
Centralized governance of certificates and cryptographic assets: discovery, inventory, renewal orchestration, compliance, client PKI, crypto-agility and AI-assisted operations.

A local web automation engine for ACME certificate issuance and renewal, designed for customers who want operational control on their own infrastructure.
Manual tracking does not scale when certificates, validation data, deployment targets and algorithms evolve on different timelines. The operating model has to become automated and observable.
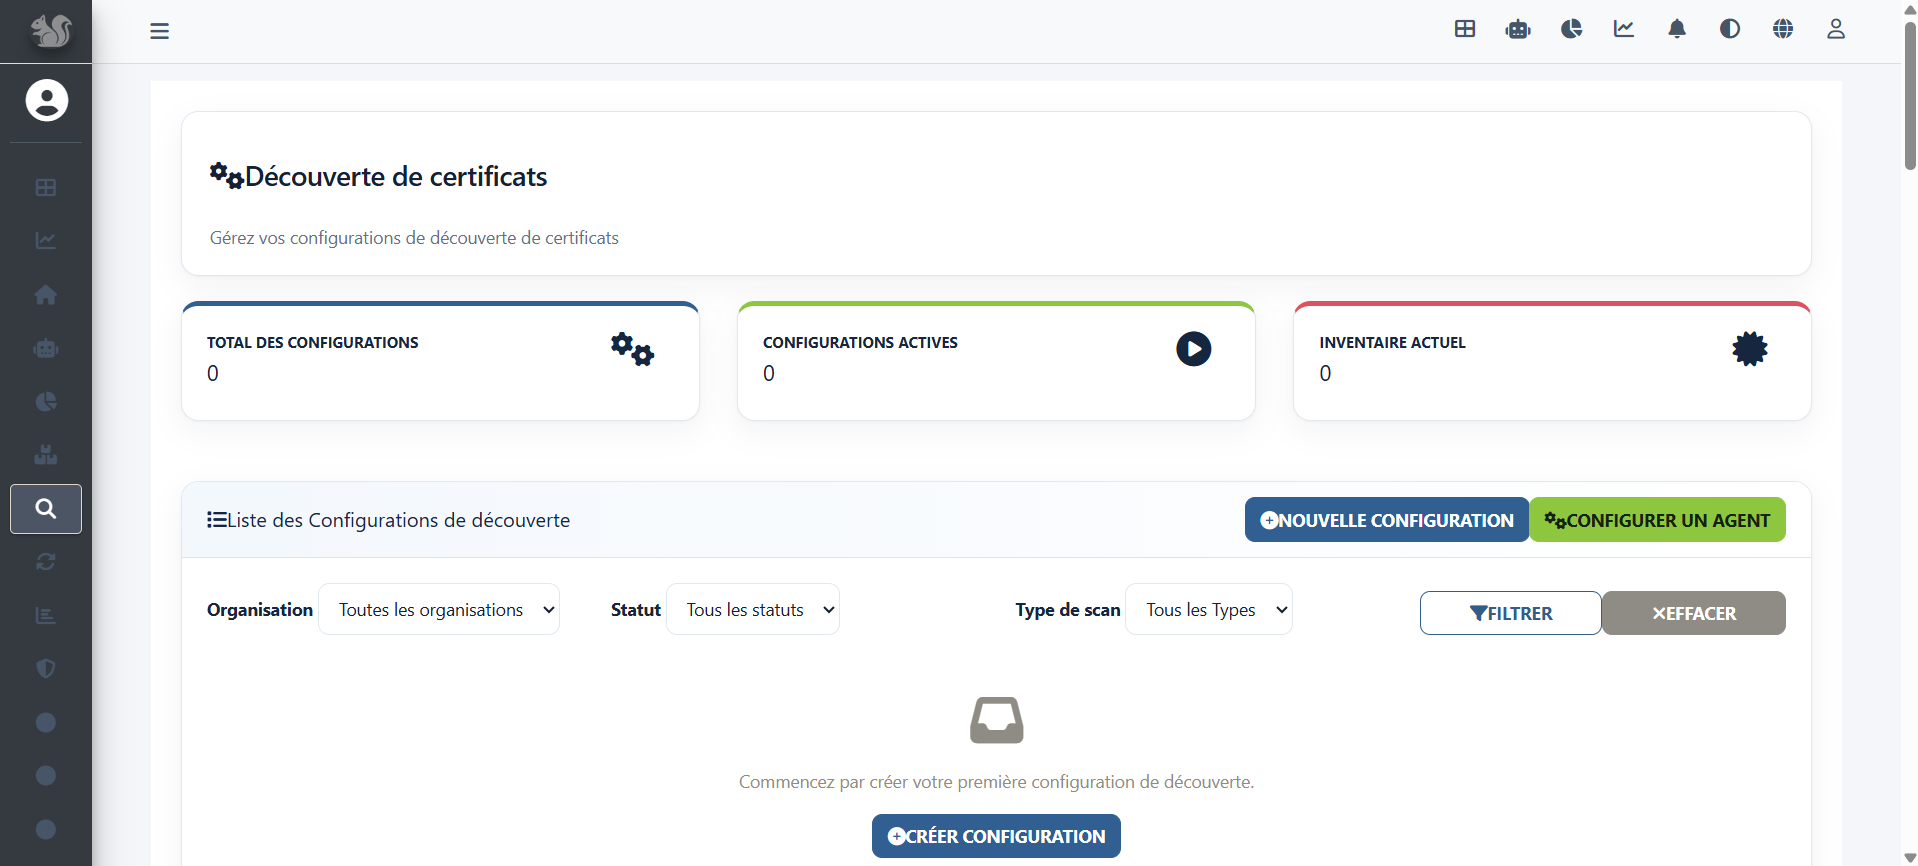
Understand the cryptographic shifts →Discover public and internal certificates as well as cryptographic assets, including local CBOM observations, and bring findings into governed inventories.

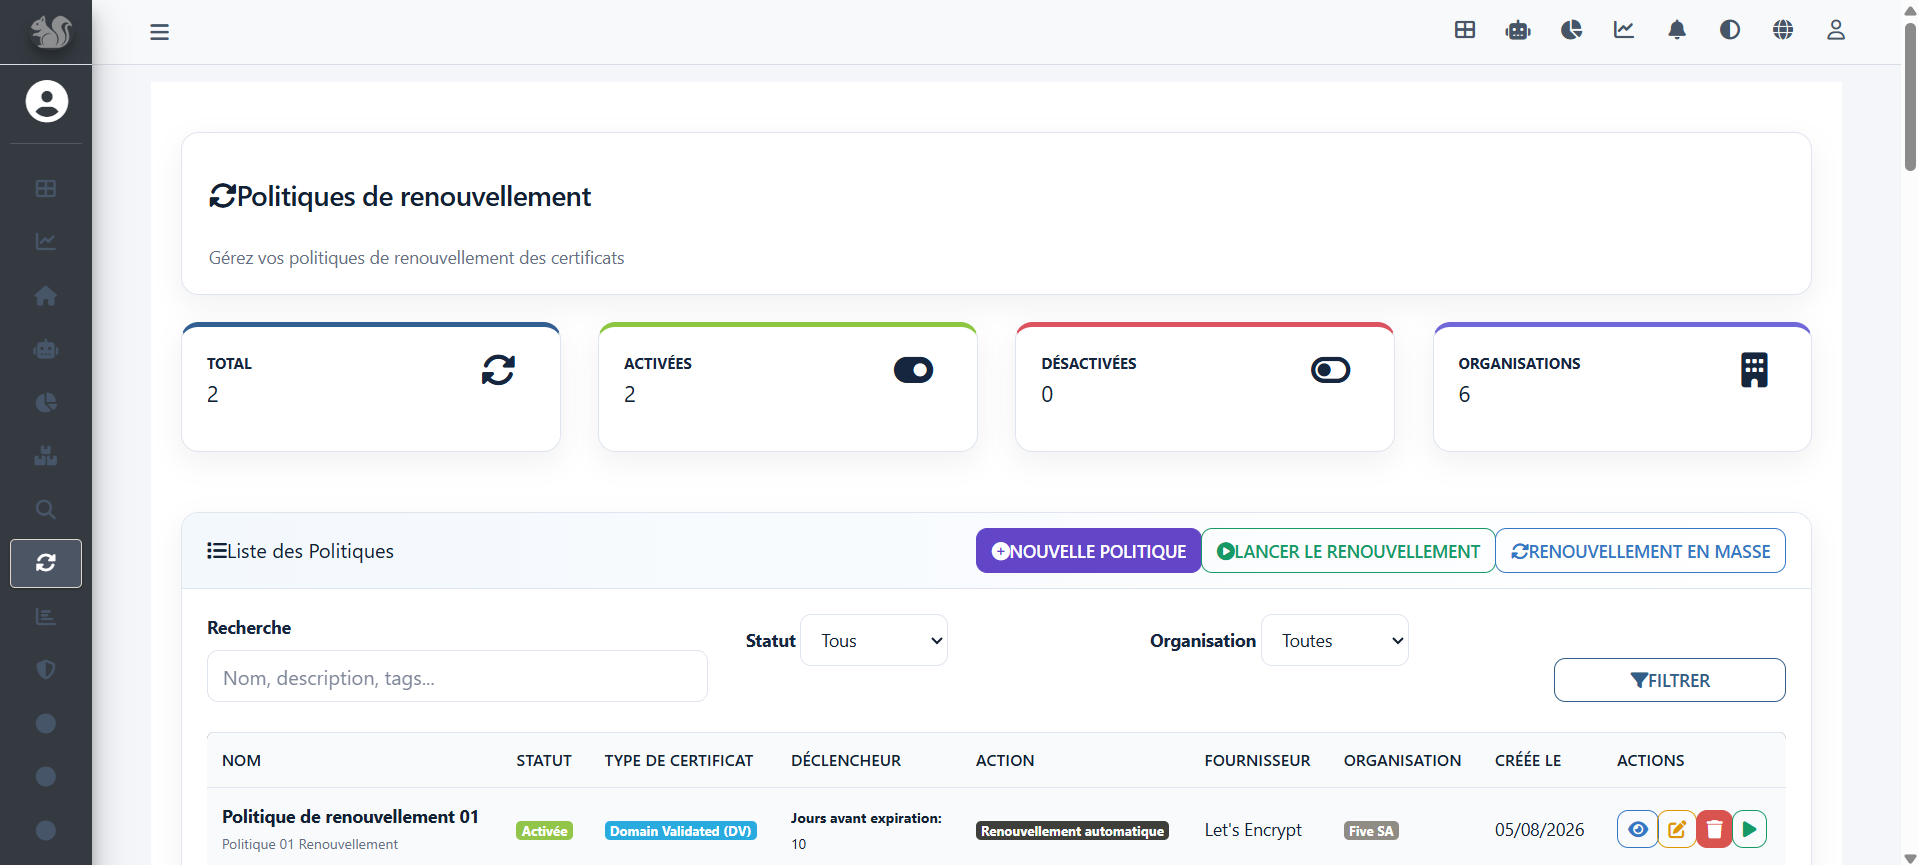
Policy-driven renewal with DNS, ACME, cPanel AutoSSL and deployment verification.

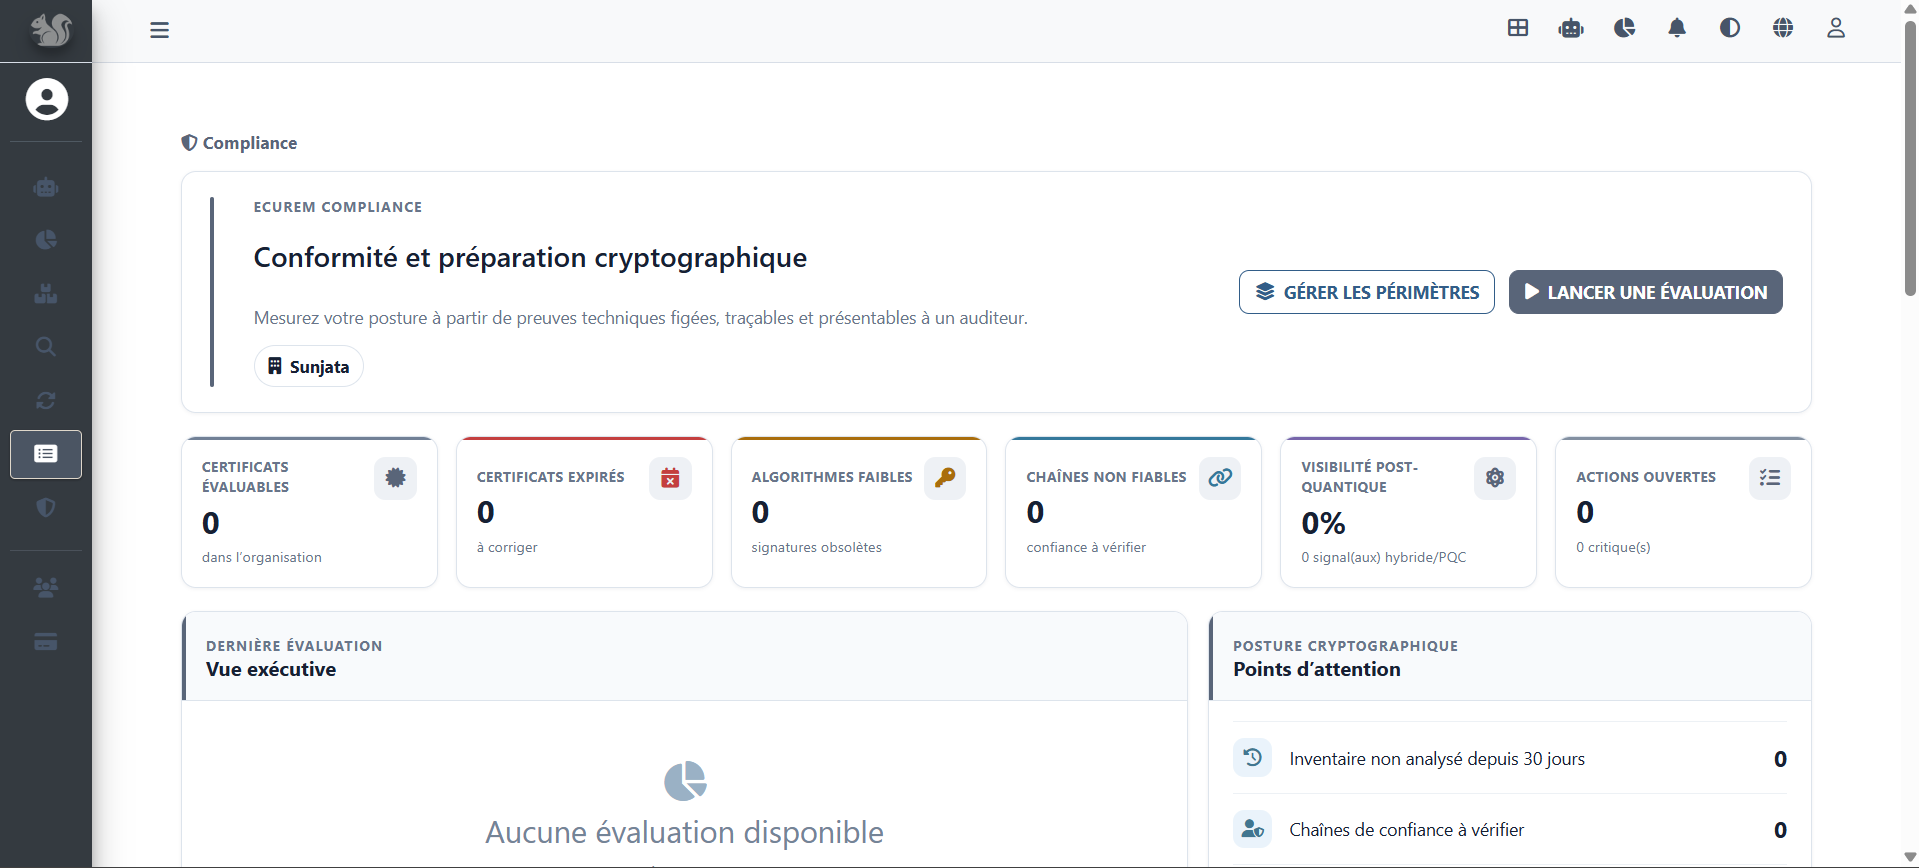
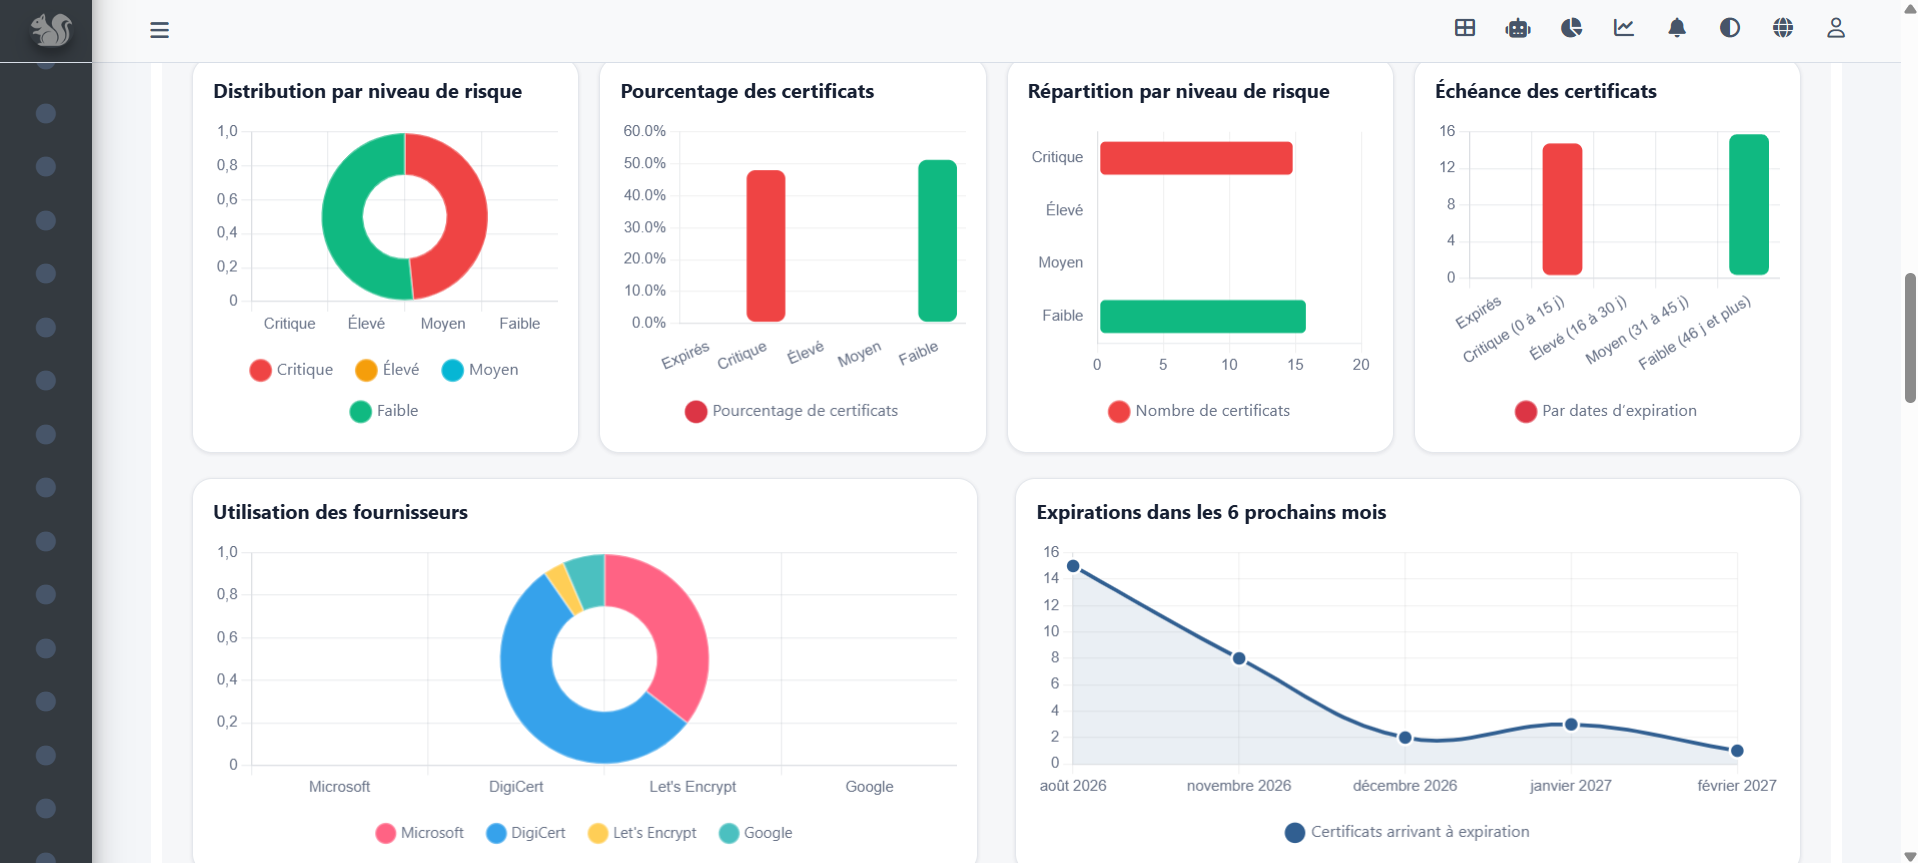
Track policy posture, exceptions and cryptographic hygiene in one place.

Ecurem CLM combines operational assistance, internal trust management and proactive alerting around the same governed inventory.
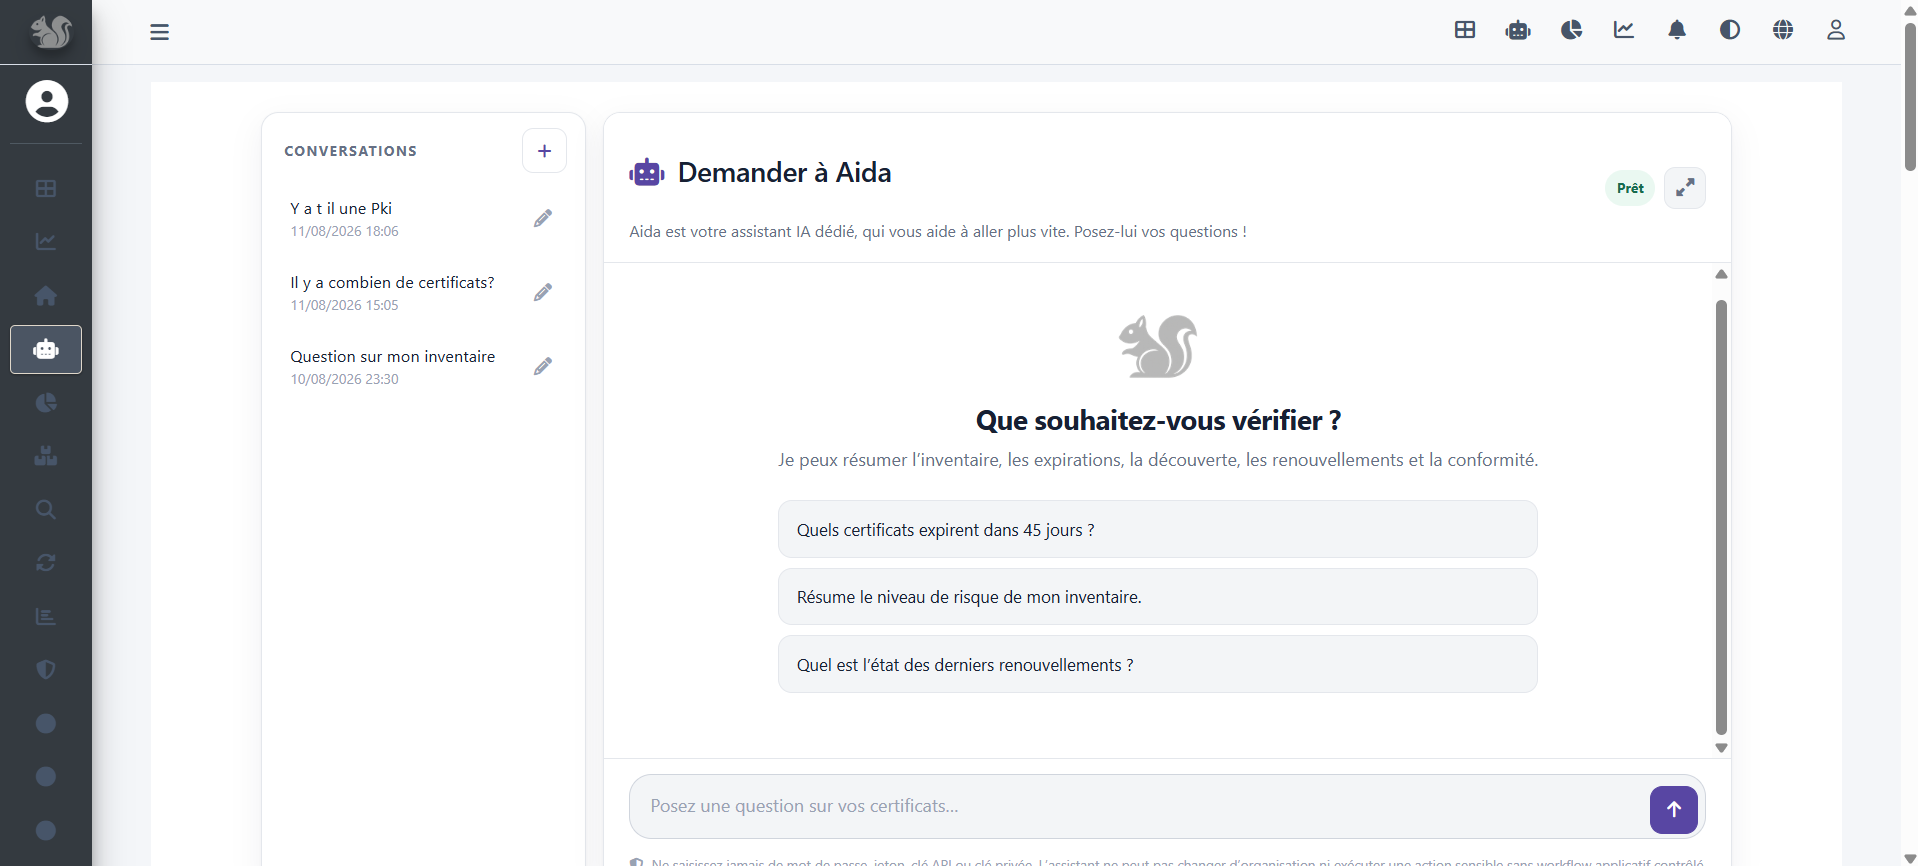
Use natural language to summarize certificate inventory, cryptographic assets, expirations, discovery, renewals and compliance while preserving organizational data isolation.
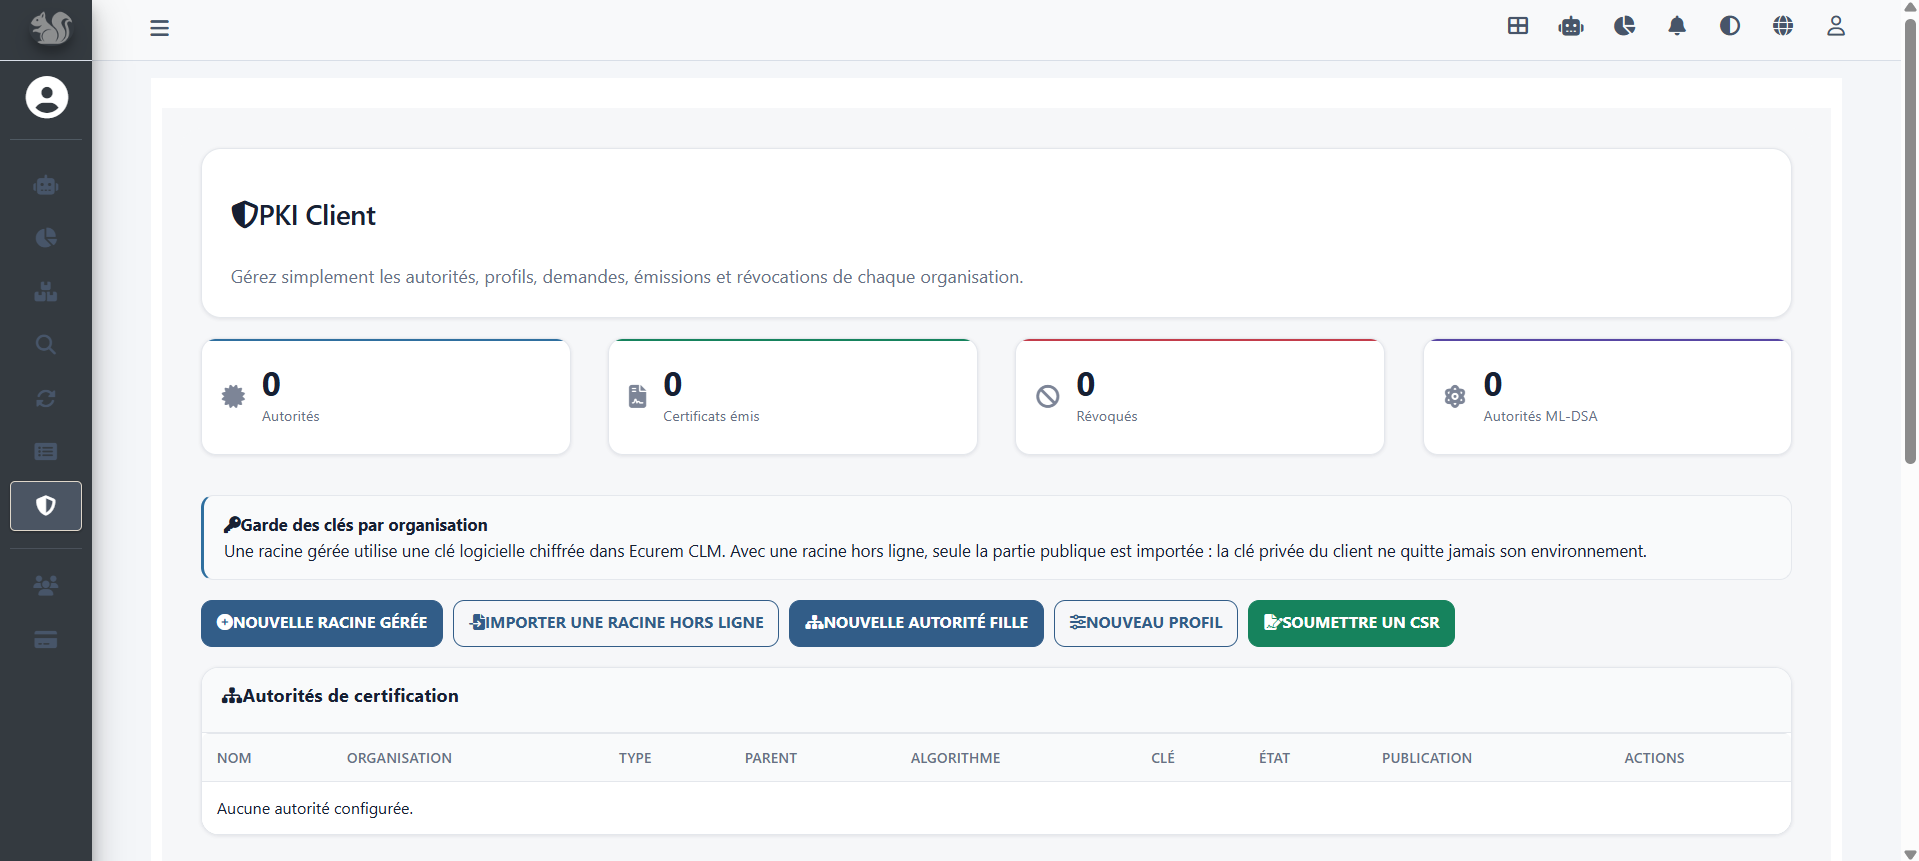
Manage private certificate authorities, profiles, requests, issuance and revocation alongside public TLS operations.
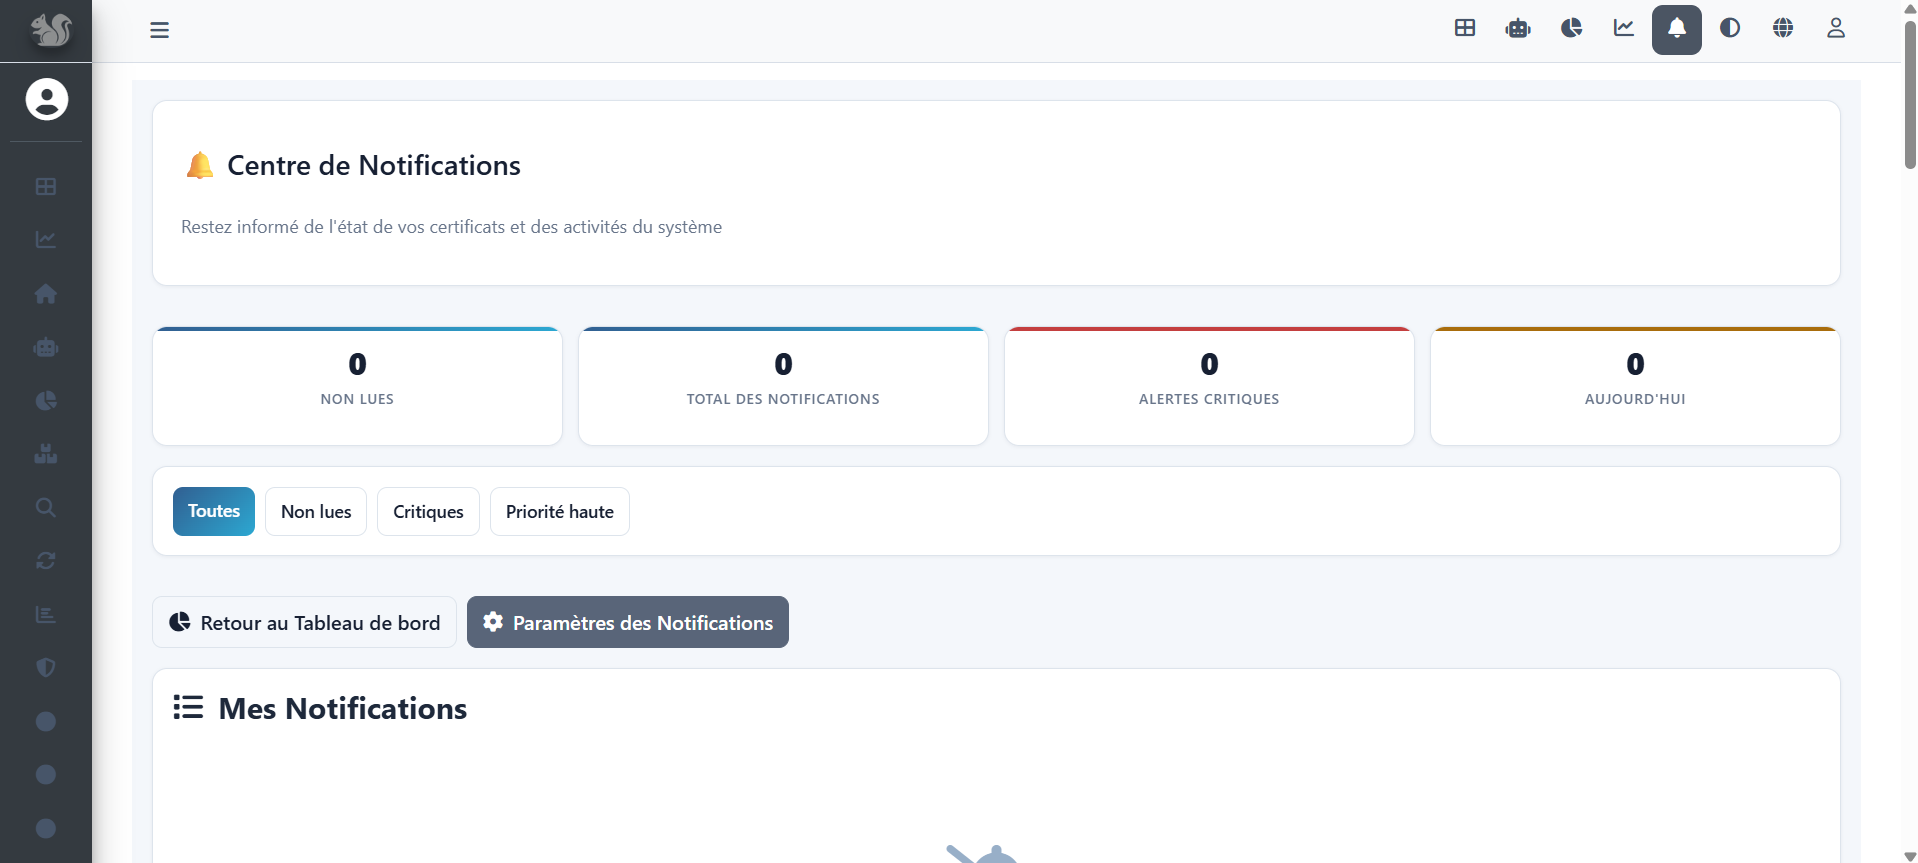
Centralize alerts and certificate activity with prioritization for critical events.
NIST has standardized ML-KEM, ML-DSA and SLH-DSA. The practical challenge for organizations is now inventory, dependency visibility, prioritization and controlled transition.
Explore crypto-agilityGuides, policies, cryptographic explainers and operational documentation remain part of the product experience — not hidden in a separate support site.
A modern cryptographic operating model should make certificates and cryptographic assets easier to govern, not harder to understand.