01 · DISCOVERY
Know what exists.
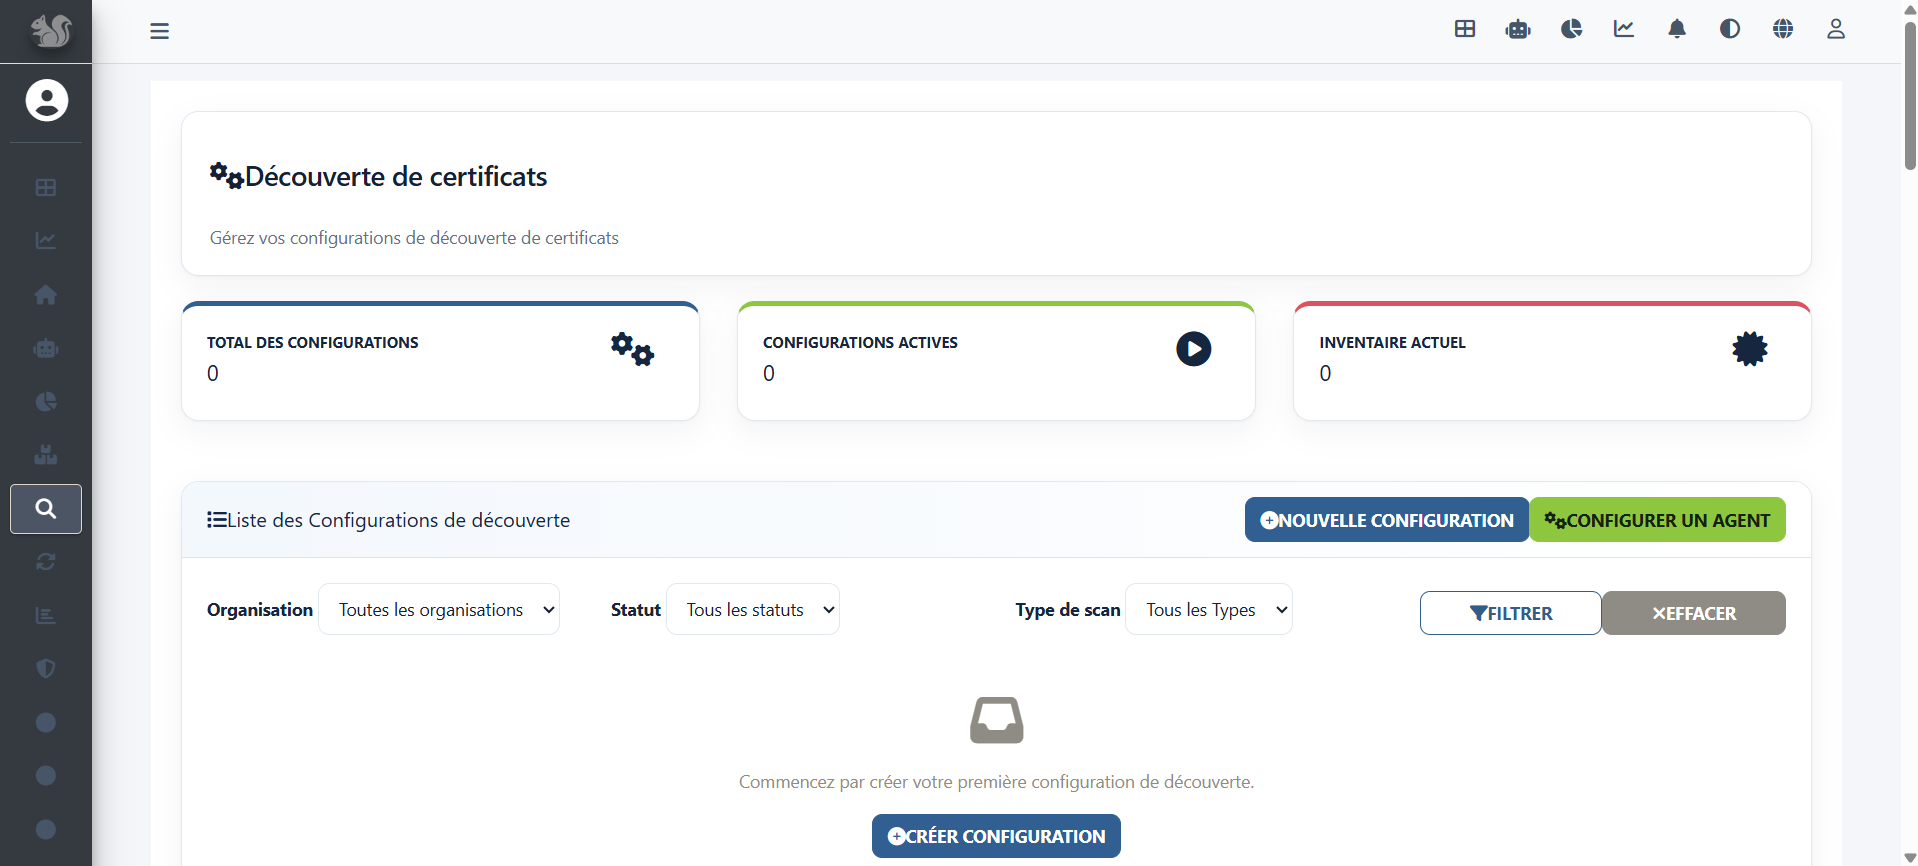
Discovery reduces blind spots by finding certificates and cryptographic assets across exposed and internal environments, including local CBOM observations, and feeding them into governed inventories.
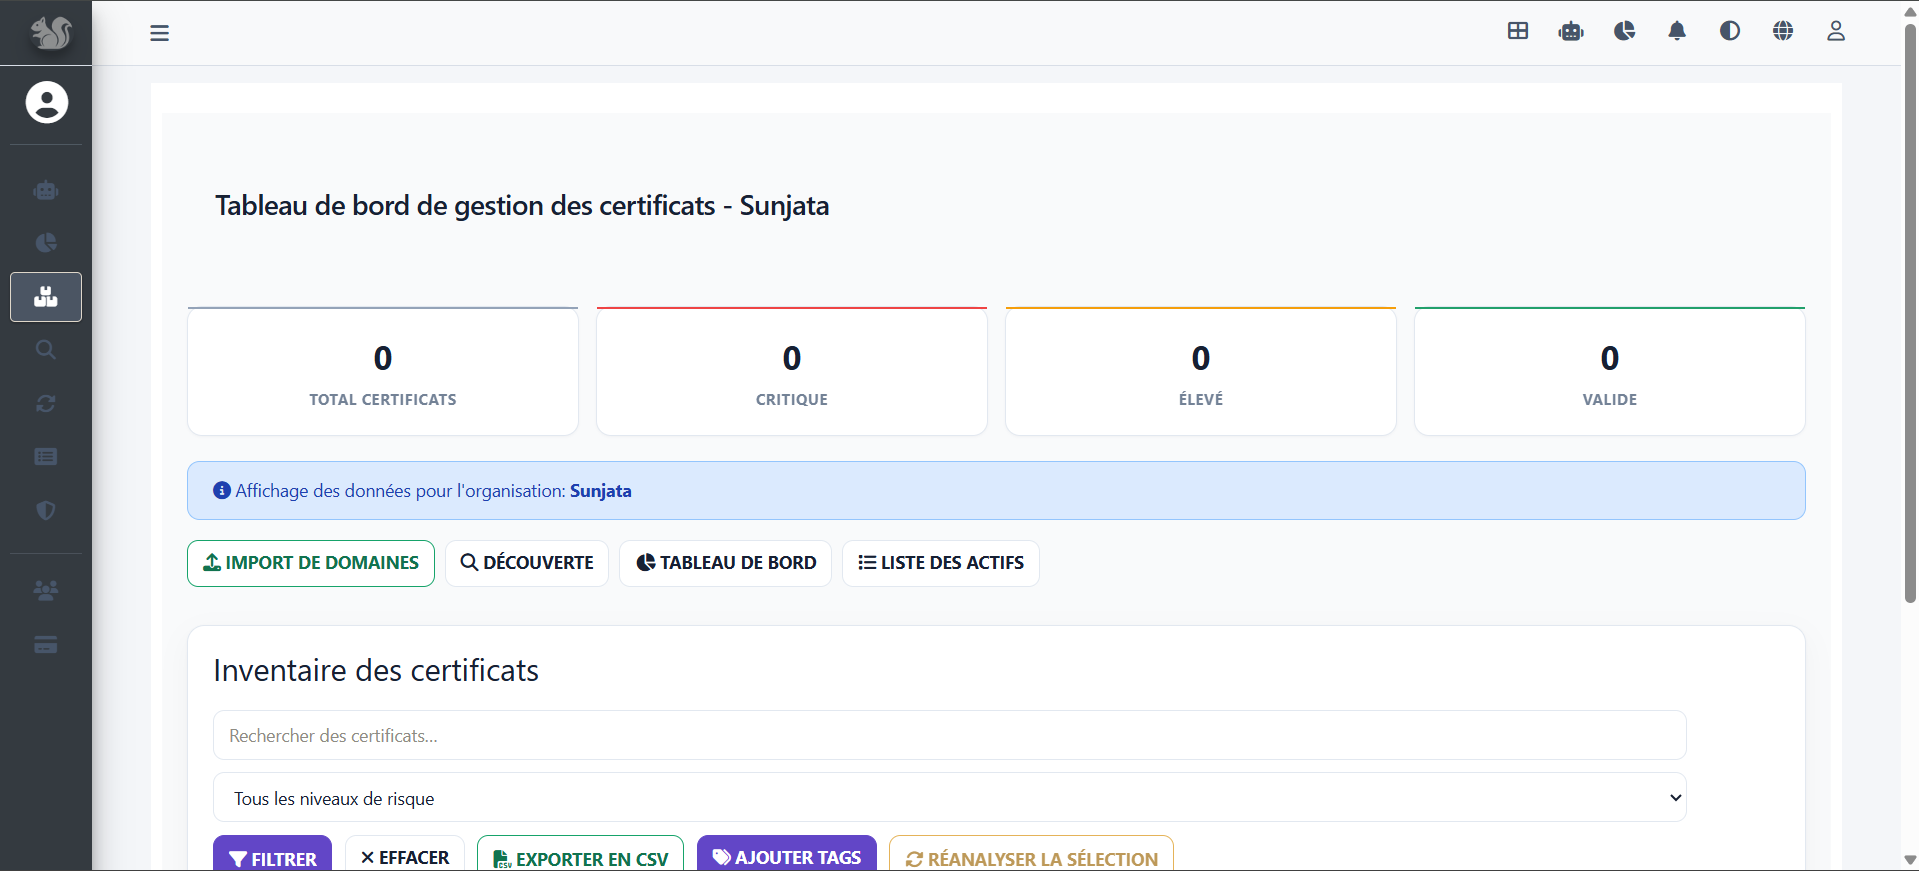
Centralize certificate and cryptographic asset discovery, inventory, renewal, compliance, crypto-agility and private PKI operations in a bilingual platform designed to make cryptographic operations observable and governable.
Discovery reduces blind spots by finding certificates and cryptographic assets across exposed and internal environments, including local CBOM observations, and feeding them into governed inventories.
Track certificates, domains, issuers, cryptographic assets, algorithms, protocols, libraries, keys, post-quantum posture, expirations, tags and ownership from one operational source of truth.
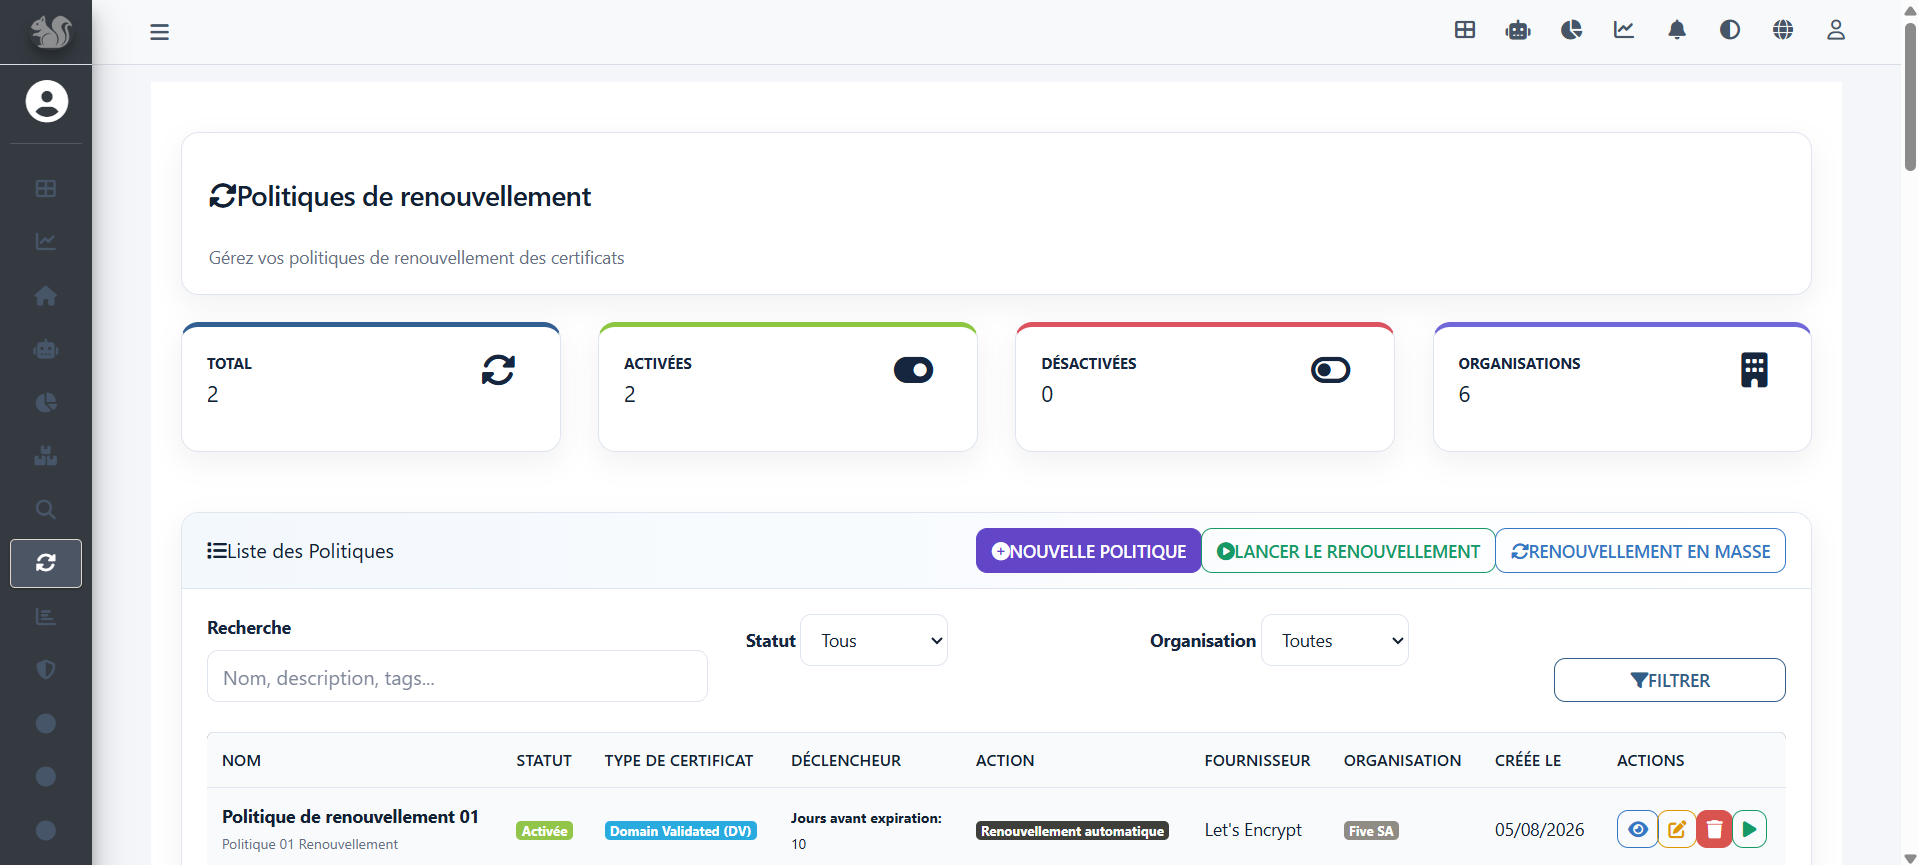
Use policy-driven orchestration with ACME/DNS workflows, cPanel AutoSSL delegation and independent post-deployment TLS verification.
Bring policy evaluation, evidence and exceptions closer to certificate and cryptographic asset operations.
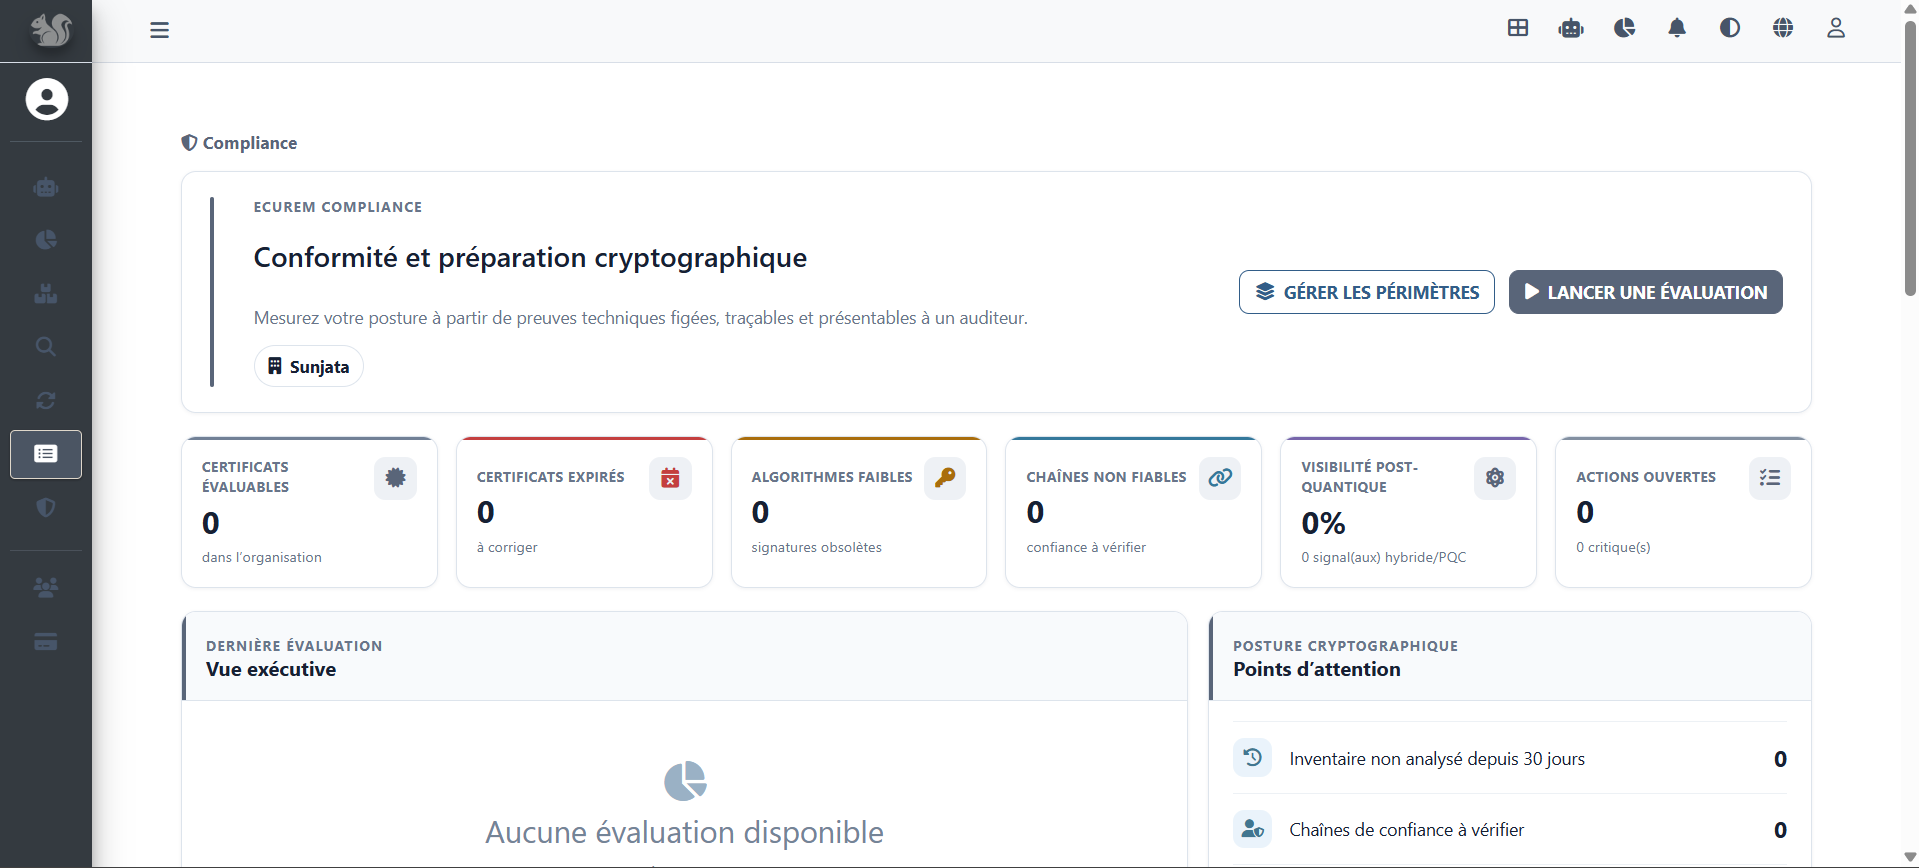
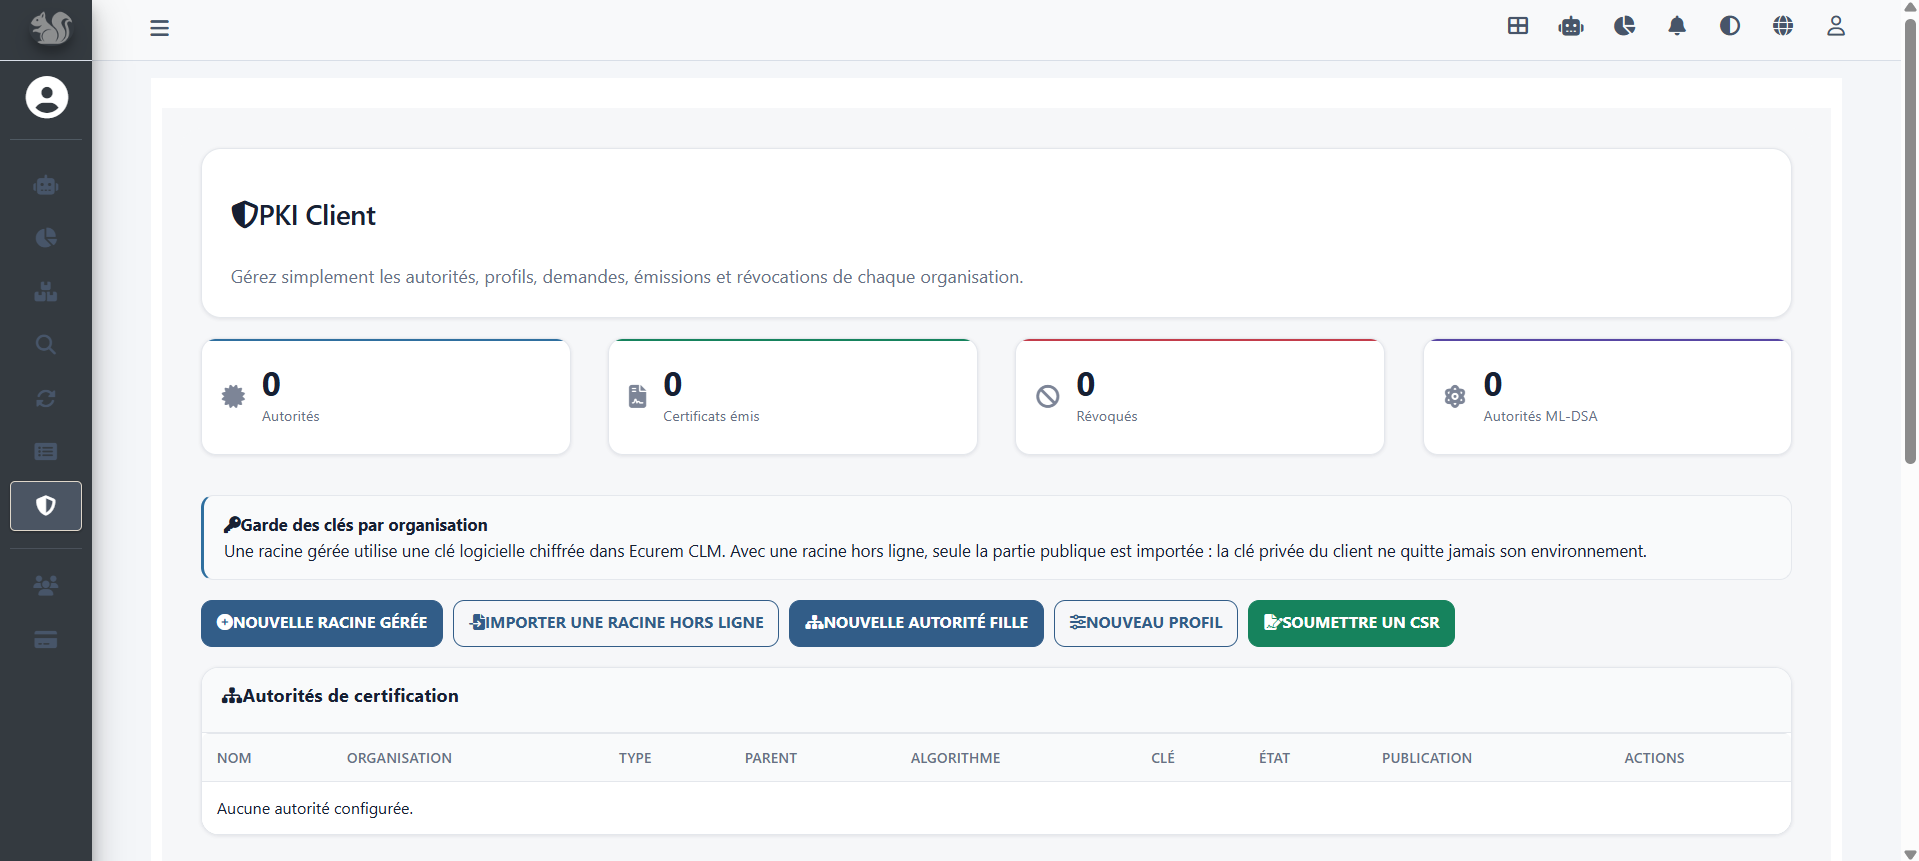
Operate internal certificate authorities and private certificate workflows alongside public TLS governance.
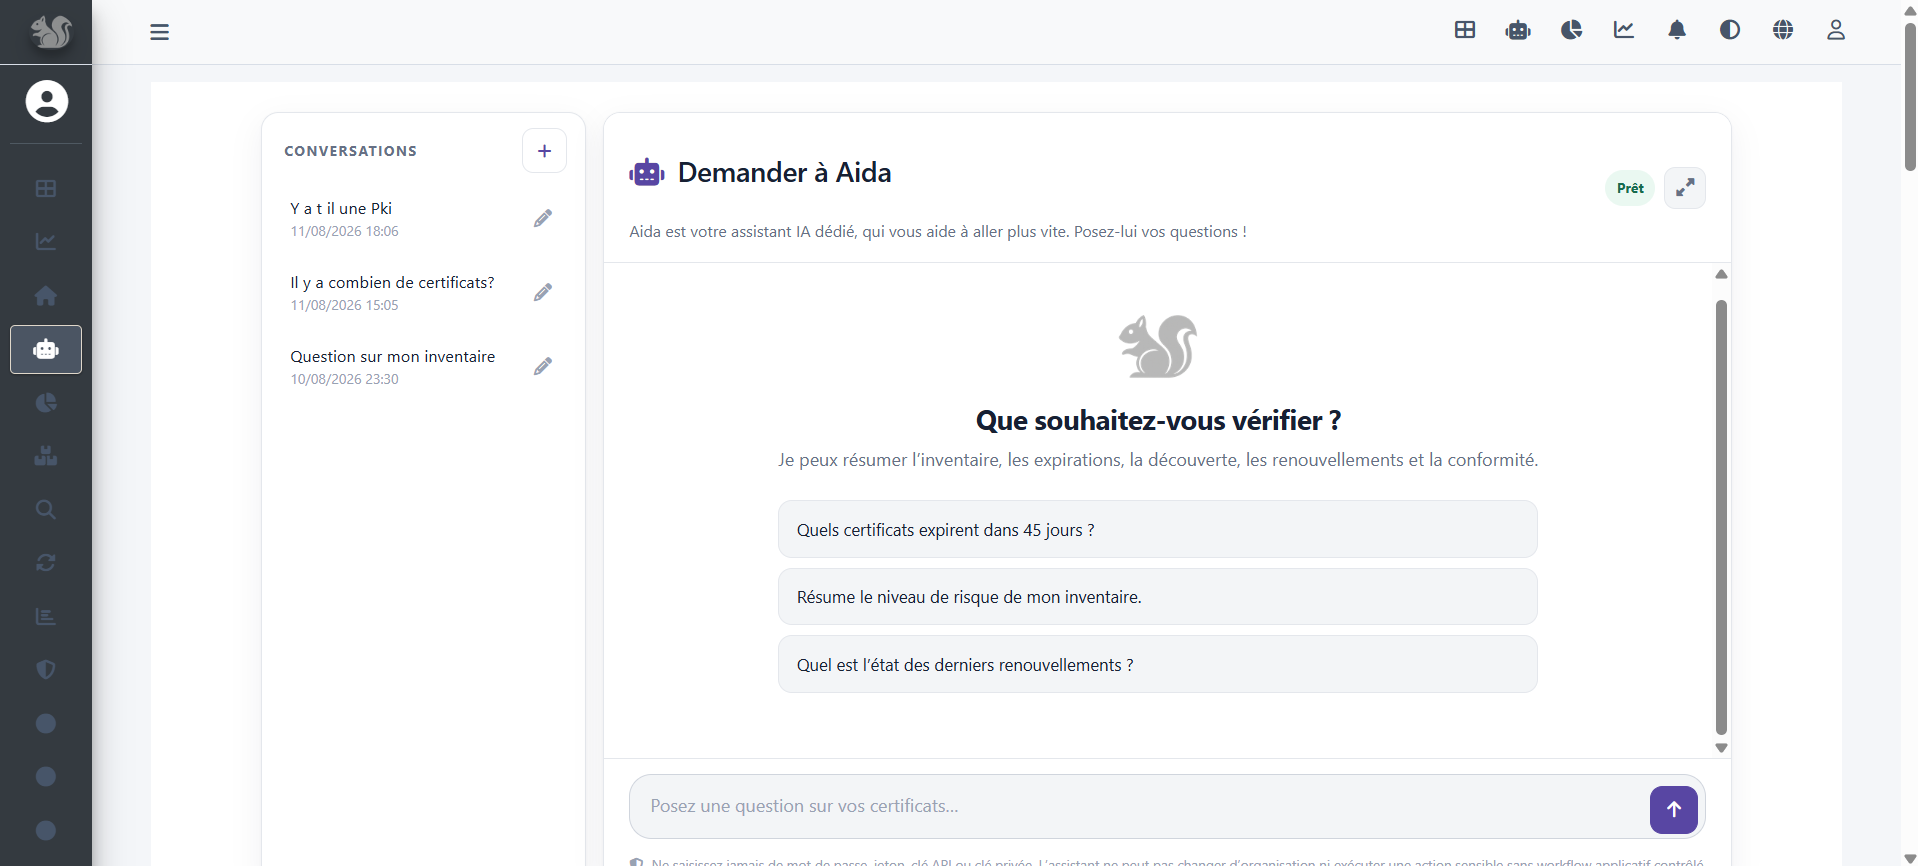
Guide users through platform actions and operational questions without turning the CLM into a black box.
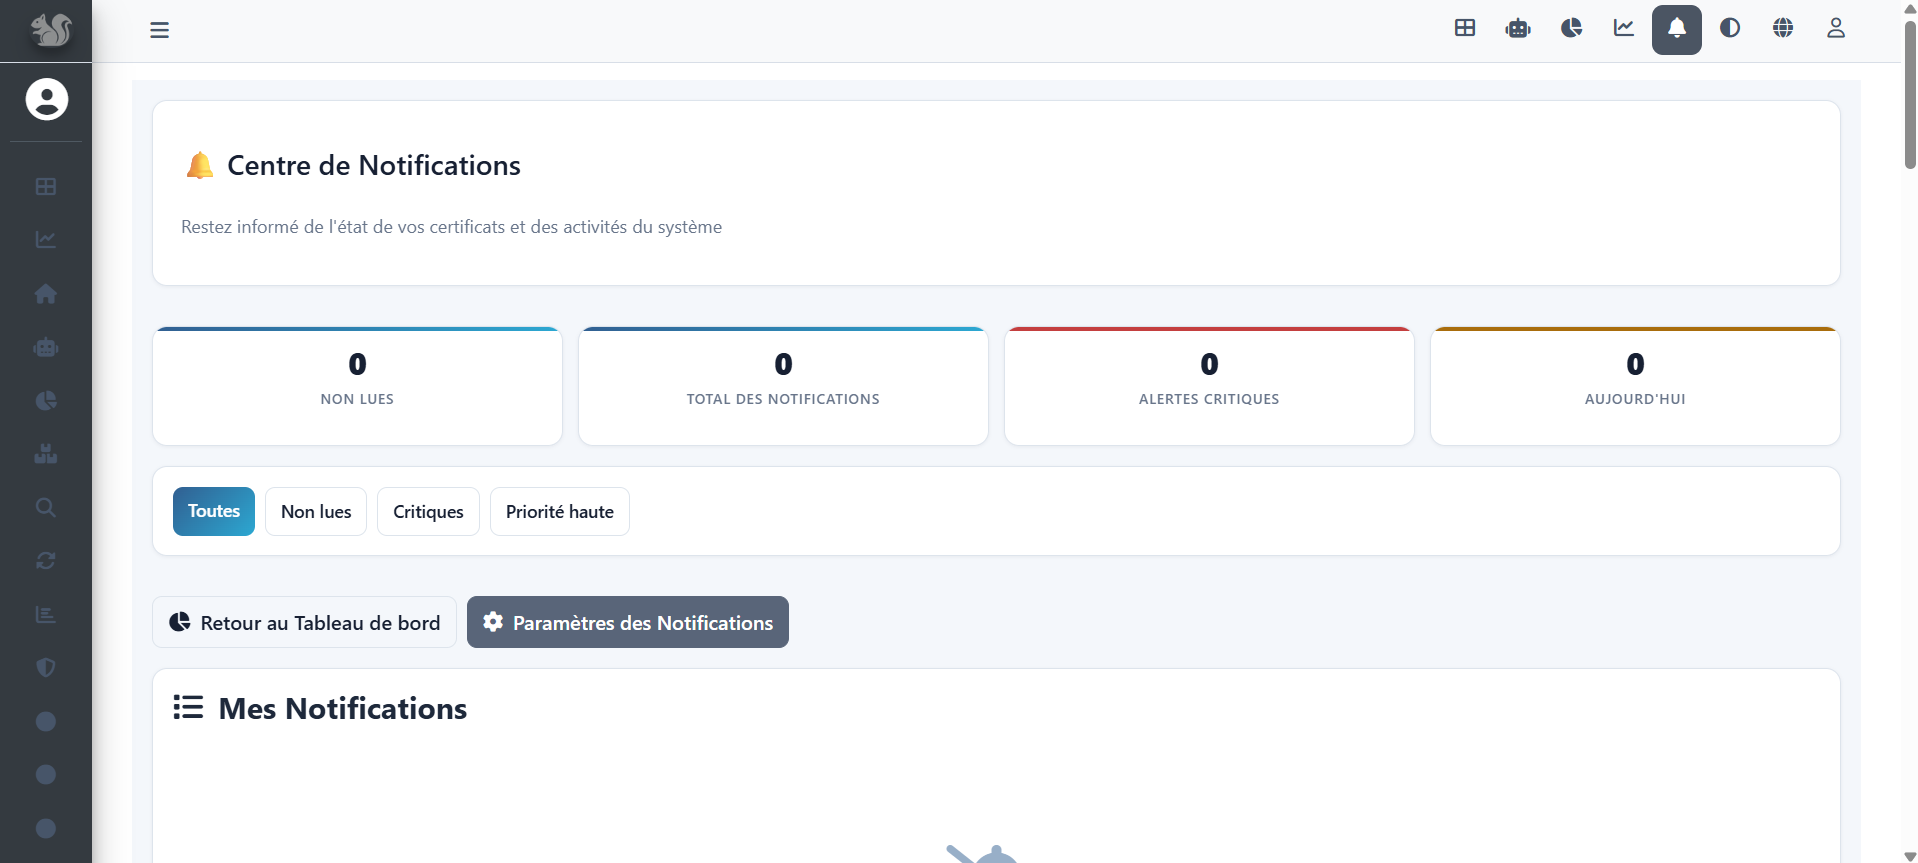
Centralize unread, critical and high-priority certificate notifications so teams can react before service continuity is affected.
One platform, with deployment models adapted to security, sovereignty, data residency and operational requirements.
Use Ecurem CLM as a managed cloud service without having to operate the underlying application infrastructure.
Run Ecurem CLM on a dedicated instance hosted according to your operational and data-location requirements, including hosting in Quebec or Canada when required.
Deploy Ecurem CLM in your own infrastructure, private cloud or controlled environment when architecture, security or sovereignty requirements demand it.